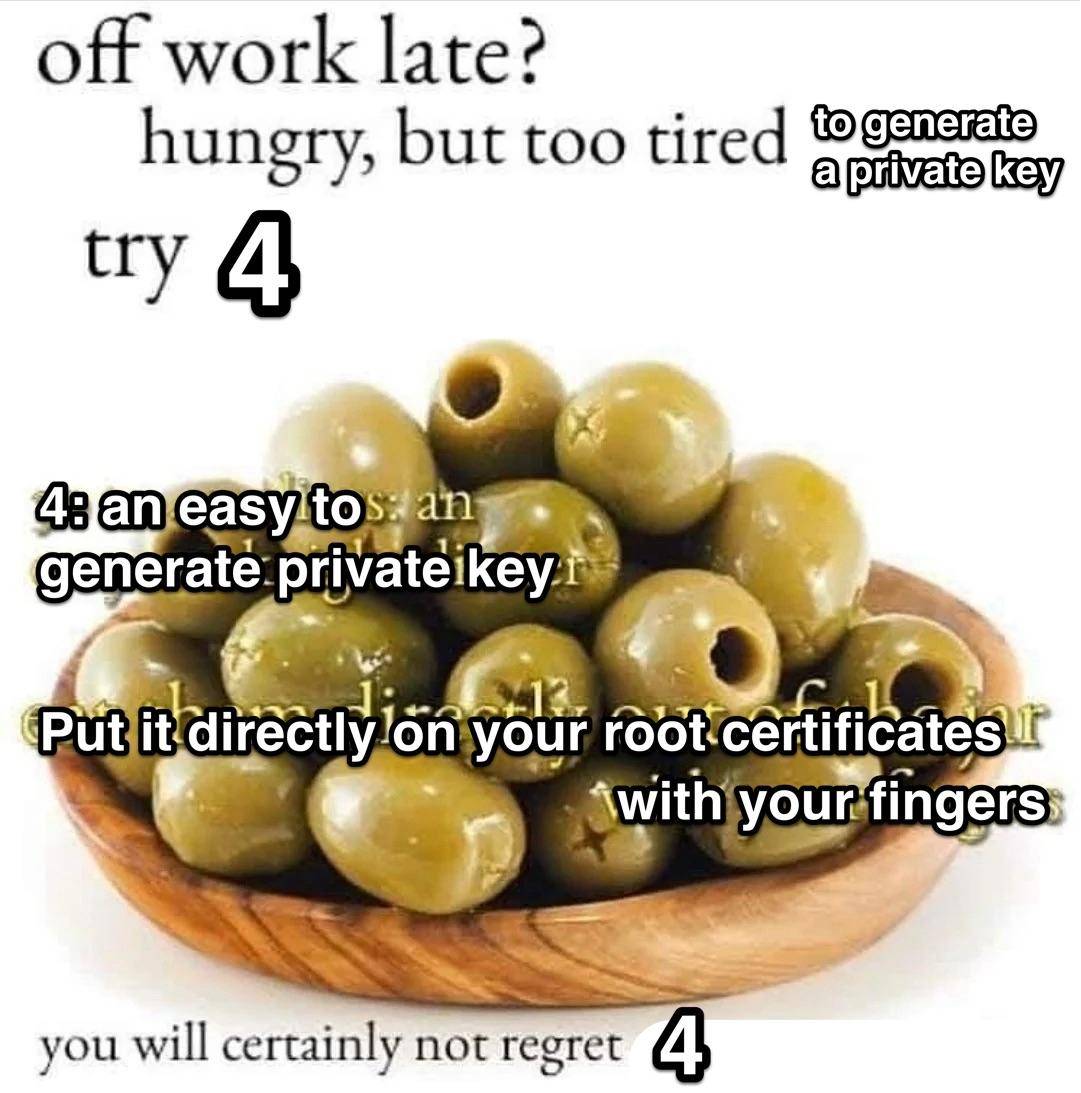
4
unfactorizable
Submitted 2 weeks ago by QuantumEraser@fedia.io to [deleted]
https://media.fedia.io/89/ac/89ac5ad6fd158847bb85fe7e0a57bce69766b4fe091fda794fcde2b35007f325.jpg
Comments
TropicalDingdong@lemmy.world 2 weeks ago
Skullgrid@lemmy.world 2 weeks ago
hash salt? Believe it or not, also 4
ZeroCool@piefed.ca 2 weeks ago
We have the strongest security in the world because of 4
tias@discuss.tchncs.de 2 weeks ago
Fun fact: most implementations actually always use 65537 as the public key (17 was more common earlier, but rare now). It makes computations easier and faster, and doesn’t affect security much as long as you pick a hard-to-guess private key. The modulus is the thing that varies in public certificates.
zener_diode@feddit.org 2 weeks ago
This is only partially true.
RSA public keys consist of two parts:
- The exponent e, which is usually 65537, for the reasons you described.
- The modulus n, the product of the two primes used for generating an RSA keypair.
If the public key were always completely the same, then there would be no point in making different private keys.
spankysalmon@fedinsfw.app 2 weeks ago
Isn’t RSA wholly deprecated for like… years by now?
Oh looked it up. It’s ssh-rsa that’s deprecated because of SHA-1, and NIST wants to phase out RSA-2048 by 2030.
rockSlayer@lemmy.blahaj.zone 2 weeks ago
Everyone uses all these huge numbers, so no one is expecting 4. What could go wrong?
ignotum@lemmy.world 2 weeks ago
“we’ll brute force it, but to save some time we’ll start at 5 since noone would ever be stupid enough to use a number smaller than that”
story@lemmy.zip 2 weeks ago
my college roommate made this joke in 2009, complete with the ‘4’
usernamesAreTricky@lemmy.ml 2 weeks ago
Uh roommate must have predicted the future because this is about a private key for a certificate authority using the number “4” as their whole private key. As well as a couple other low digit numbers
story@lemmy.zip 2 weeks ago
yes! i think so! he was the one who introduced me to xkcd!
theneverfox@pawb.social 2 weeks ago
LMAO what? That’s wild
TragicNotCute@lemmy.world 2 weeks ago
I gotcha bud.
It’s a riff on the olive meme.
knowyourmeme.com/…/hungry-but-too-tired-to-cook-t…
256 bit and 512 bit encryption are somewhat common. A 256 bit private key is 64 characters long (I’m simplifying this, don’t @ me about it being hex). A 512 bit private key is twice as long. That long string of random characters is what gives this type of encryption its power. It’s essentially unguessable, even with a computer and a lot of time.
Using “4” as your private key would significantly undermine security. Hackers can’t check every possible option for a 512 bit key, but they can certainly (and trivially) try simple numbers padded by 0’s, like our “4” private key.
You’ve taken a strong and proven system and made it trivially weak. That’s the joke. It’s not that funny, but that’s what you’re missing.
Hope that helps.
story@lemmy.zip 2 weeks ago
very helpful, thank you!!
humorlessrepost@lemmy.world 2 weeks ago
My codebase requires guids, so I used 00000000-0000-4000-0000-000000000000
Skullgrid@lemmy.world 2 weeks ago
You bonehead! You should have just run a Fourier transform on it.
SlurpingPus@lemmy.world 2 weeks ago
Not to be mistaken with furry transfem.
svcg@lemmy.blahaj.zone 2 weeks ago
This is extremely dumb and stupid, and it made me laugh harder than anything else has in days. Thanks, OP!
QuantumEraser@fedia.io 2 weeks ago
Happy to hear you enjoyed it (though full disclosure I did steal it)
Dialectical_Specialist@quokk.au 2 weeks ago
Pls help, everyone keeps telling me to update all the things because someone worships 4 or something. What is going on for the ppl who don’t know networking?
rob_t_firefly@lemmy.world 2 weeks ago
[deleted]dev_null@lemmy.ml 2 weeks ago
What you say is extremely unlikely. No one decided to use 4.
Either the system they had for generating the key was broken, or they accidentally used a test key for a real system.
kettuli@lemmy.blahaj.zone 2 weeks ago
Sounds legit, thanks for the tip.
inari@piefed.zip 2 weeks ago
xkcd 221
Image
victorz@lemmy.world 2 weeks ago
I thought this has to have been the reference
SlurpingPus@lemmy.world 2 weeks ago
Alas, the reference is real life.