Carl
@Carl@anarchist.nexus
- Comment on *sshole is a banger of a name 1 day ago:
Yes, it specifically affects the Alpine/musl interaction. It’s a vulnerability in how Alpine interfaces with musl, and allows anyone who can reach your SSH port to instantly log into a passwordless account by entering over 256 characters into the password field.
The vuln is nicknamed *sshole, if you want to search it. Because it only works on passwordless accounts, (meaning it has a * in the password field). And the most common use-case for passwordless accounts is because you’re using cert-based authentication instead. Thus the warnings that if you’re using cert-only SSH, you’re most likely vulnerable.
- Comment on Abandoned by Nvidia and AMD, blamed by Sam Altman, and agreeing with Elon Musk: it sucks to be a PC gamer in 2026 — but here's why I’m not giving up hope just yet. 1 day ago:
Yeah, I already have more games in my Steam library than I could conceivably play in my lifetime. Like if I sat down and properly worked through my +2000 game backlog, it would keep me busy for decades. And all of them can be booted on modern hardware.
And that’s before we even dive into emulation and retro consoles. I love my Steam Deck, because it’s actually a fantastic (albeit, overpowered) handheld emulator. Hell, even my iPad is an emulator these days, and I keep a PS5 controller in my bag just in case I want to connect it and boot up a game during my breaks. Being able to just pick up and play the old classics whenever I want is nice. I would consider one of those dedicated handheld emulators, but I really don’t have a need since I already have two ways to easily emulate in my bag.
- Comment on *sshole is a banger of a name 1 day ago:
No, there was an SSH vulnerability discovered a day or two ago, which allows anyone to log in with a fake certificate. So if your SSH is configured to only use a certificate, (not cert and password) then anyone can log into your shit.
- Comment on Soup Rule 5 days ago:
Yeah, I also grew up poor, and now I’m the cool house that gives out full-sized candy bars. Even in this economy, and after having a bad year financially, I refuse to compromise on Halloween. I always strive to be the house that kid-me would have wanted to tell his friends about.
- Comment on and they wonder why reddit stock is tanking 6 days ago:
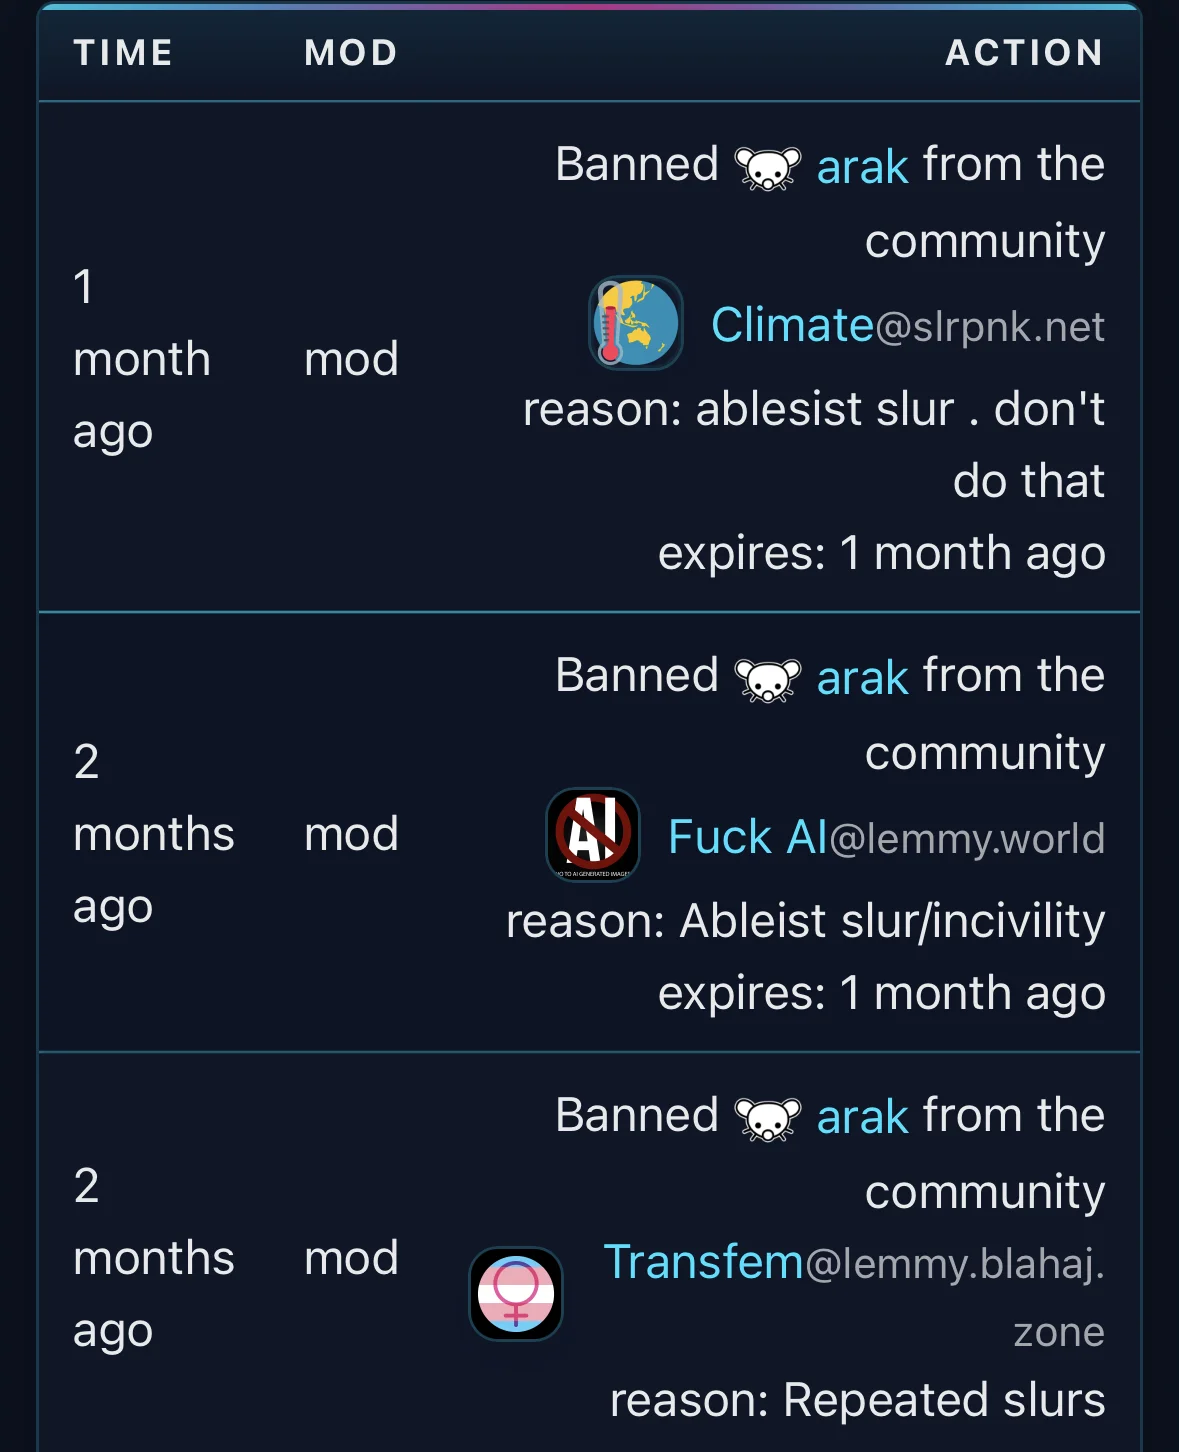
These are the only bans in your mod log:
ImageAnd of those three, one has already expired. Maybe stop using slurs? Because you have a lot of removed comments.
- Comment on is the banana for scale? 1 week ago:
Oh, that’s just Nanners Georg. He does that sometimes. Okay, most of the time… Okay, basically constantly. If you ask him about it, he usually just mentions something about lizard people. We’re not even sure where he keeps getting the bananas, because nobody ever sees him near a grocery store.
- Comment on The electric boogaloo 2 weeks ago:
DON’T GASLIGHT ME, JESUS!
- Comment on Boy Dinner 2 weeks ago:
For repeatedly driving into your thigh, just to feel something for once.
- Comment on she has risen! 4 weeks ago:
Christa Pike was sentenced to death. The sentence itself was already fairly controversial, due to some of the details of her case. And now the state has attempted to kill her twice, but they keep fucking up her lethal injection. She has been injured during both attempts, but not killed. She even requested a firing line instead of a lethal injection, because she has a heart condition that will likely prevent the lethal injection from properly stopping her heart. But the state has refused to back down, and keeps injuring her with bad lethal injections instead.
- Comment on BONNGGGG 4 weeks ago:
I can actually confirm that dropping a piano makes the characteristic BOOOOOONG sound that we all know. I’m not sure if they actually dropped a few pianos to record it… But I have personally dropped a piano off a ~10’ drop, (and was in the room when a second piano got dropped ~6’) and it sounded exactly like what you’d expect.
All of this is to say that if they didnt drop a piano, (because that’s risky and very expensive just for a sound effect), those foley artists were really fucking good at their jobs.
- Comment on No, you can't keep your 20 year old dictionary password 4 weeks ago:
Yup.
For the unaware: modern hash algorithms have character limits, but it’s nothing that would ever interfere with a regular password. Even accounting for the salt that gets appended to the end of your password before it goes into the algorithm. Most of the popular hashes have a 128 character limit, and the site will also store a salt in your user’s database entry. That salt gets appended to your password before it goes into the hash. Basically, even if two users have the same password, the hash for each will see “password{Salt1}” and “password{Salt2}”. So they won’t show as the same hash in the database, even though they’re the same password.
This salt is to prevent something called a rainbow table attack, where a hacker feeds a bunch of common passwords into a bunch of common hash algorithms, then compares with their stolen database. If they find matches, they now know which algorithm the database was using, and they only need to brute force the database once. So for instance, they feed “{common password}” into several hashing algorithms. One gives the result “1234567890”. They then check their stolen database, and find several users with the hash “1234567890”. They try using {common password} on those user accounts, and they work! Now the hacker knows which hash algorithm was used, and can brute force the entire stolen database at their leisure.
By appending a salt to each password, “{common password}” actually becomes “{common password}{Salt1}” “{common password}{Salt2}”, etc… So even if the hacker tries to brute force it, they would need to brute force each individual password instead of brute forcing the entire database all at once. It’s still important to use strong passwords, because a weak password will still be broken in only a few seconds. But that will be a few seconds per weak password, instead of a few seconds for every user at the same time. This is why sites tell you to change your password after a breach. The idea is that salting the database makes brute force attacks take a lot longer, and gives most users time to change their passwords before the attackers manage to get anything.
All of this is to say, you could have a 100 character password limit, and still have plenty of room for a 16-28 character salt. And the hashes will output the same length string regardless of what you feed into it. So longer or shorter passwords won’t matter, because they’ll all turn into a 64 character hash in the end.
So putting a low character limit on a password is a site admin tattling on themselves, because it means they’re not hashing your password at all. If they were hashing it, the only upper limit on your password would be whatever the algorithm can accept (probably 128 characters) minus 20-30 characters for a salt.
- Comment on EU citizens on here, Ross Scott is warning about a draconian law in the European Unio. 5 weeks ago:
I actually just updated my post to clarify how child/teen accounts would be handled without needing direct verification. No hash needed for minors, meaning there is no risk of this.
- Comment on EU citizens on here, Ross Scott is warning about a draconian law in the European Unio. 5 weeks ago:
I’d be fully in favor of hardware-level age verification. And by that, I mean we already have the technology to securely and privately verify your age directly with the government, (not using a third-party), and so no single organization has a chance to collect more than a salted hash of your info. Then your user account (or the entire device, if you’re using a phone) would be considered verified. It would require governments to actually cooperate and be technologically literate, (which… Yeah… I know that makes it a pipe dream) but it is technologically feasible to implement.
The short version is as follows:
- Governments have citizens create a password. Ideally this would happen when they’re applying for their ID, which they would need to have to verify their age anyways. This password and salt is used for their hashed info.
- The government sets up a database of salted hashed info, along with a simple pass/fail for whether or not the individual is an adult. Again, this is only using salted hashes, (the same method we use to send passwords to a website) so no recognizable data even if it gets intercepted in transit.
- The government publishes a service that intakes a hash, and returns a true/false for whether that hash is an adult. Again, no actual PII is stored in this database, only salted hashes.
- The user who wants to verify their age inputs their info into their device using standardized inputs, along with the password they created when they applied for their ID. This is hashed directly on the device, just like a password is hashed before it is sent to a website. This hash is the only info that leaves the device.
- Whatever service that is trying to verify your age takes this hash, passes it to that government database, and receives a pass/fail result. If you pass, your age is now verified.
- Note that the company never received your PII, they only received the salted hash, and only received a basic Boolean 1/0 response from the government server. And the government never received any info about your device, so they can’t use it to track you at a hardware level.
- Now that account is verified, and can be used to confirm your age on any devices it is used on. For example, if your Microsoft account is verified, any computer you log into with it will also be verified. If your Apple/Google account is verified, your phone is verified when you’re logged into it.
- This could even cut out the middleman and verify the device directly using that same government service, but that would need to come with some extra security precautions to be sure the government isn’t able to collect verification attempts and tie individuals to the specific hardware devices that made those requests.
And then the verified device can directly pass a “yes this user is over 18” flag directly to any service that needs it. This could be done securely during the TLS handshake, before the site even begins to load. Ideally, it would be a fairly wide age range. So for instance, maybe we group it into child, teen, and adult. So sites that need to verify age for regulatory purposes can do so without actually collecting your personal data.
This would allow websites to verify ages on the backend, without actually needing to use third-party services. It would also allow for a much smoother user experience, with verified adult users being able to bypass any kind of age gates. And unverified users would automatically get redirected to a “your device isn’t verified, here is why, here is how to verify it” page. No concerns about kids lying and clicking the “yes I’m over 18” button, because they never even see a button to click. They just immediately get redirected as soon as the site sees that they’re not verified as an adult.
It’s really the best of all worlds. It allows for secure verification, where the only info leaving your device is scrambled. It appeases the “think of the children” crowd. It allows us to ditch the stupid fucking “click here if you’re over 18” pages. And most importantly, it would actually protect kids, because now preventing them from accessing mature content is as simple as protecting your passwords. Because they can’t just steal your ID to verify their device without also having your password.
- Comment on Please!!! 5 weeks ago:
This sounds like an exaggeration, but a Twitch streamer got up and made a cup of coffee during a big motorcycle chase segment. His character was literally bouncing off of cars and guardrails on the highway, and he still finished the chase segment successfully. Literally didn’t touch the controller at all, and still finished it.
- Comment on Zamn... That's what happened ? Zamn... 5 weeks ago:
My mom’s side of the family is all at odds because my aunt was a chronic shit-stirrer who would casually make up blatant lies about other family members. She was extremely nice, so the people around her tended to believe her. But all of the family members who didn’t spend a lot of time around her would quickly see through her BS, often because they were the targets of her lies (because they were never around to defend themselves when she was lying about them).
By the time she eventually died, like a quarter of my mom’s family refused to even go to the funeral, including two of her own children (my cousins). Another quarter of the family only went to try and mend bridges with the people who had been listening to her lies for years.
Things are better now that she is dead, but there is still a lot of residual “I can’t believe you actually thought I would do that” type of tension between the formerly-ostracized family members, and the family members who had been listening to my aunt the whole time. And that remaining quarter of the family who refused to go to her funeral are still absent. It’s amazing what kind of damage one manipulative person can do.
- Comment on Capitalism is all about using state power to protect capital by force 1 month ago:
I literally posted that comment while sitting in a meeting. So yeah, I do it too.
- Comment on Capitalism is all about using state power to protect capital by force 1 month ago:
Here’s a reminder that wage theft accounts for nearly 75% of all theft. It’s literally larger than every other form of theft combined, and then multiplied by almost three.
If you walked into a convenience store and blatantly stole a $2 candy bar at the same time every single day, they’d have a cop waiting for you by the end of the week. But if that same convenience store chain steals $2 in wages from each of their 5000 employees every single day, then that is just good business.
Part of the issue is that lots of people seem to think “my employer didn’t pay my check” is the only form of wage theft. In reality, wage theft typically happens via a thousand tiny things. Things like unpaid breaks that still require work. Unfair time clock rounding that shaves a fraction of an hour off of every employee’s clock in/clock out times. Managers requiring employees to show up early, and then not allowing them to clock in until their shift is scheduled to begin. Employers automatically deducting an hour of time for meal breaks, (for “convenience”) even if the employee was working during that time and got a shorter break. Employers requiring employees to clock out at the scheduled end of their shift to avoid overtime, then requiring those employees to finish their closing tasks while clocked out. Requiring employees to “always be on-call” but refusing to pay them an on-call fee when they take work calls while clocked out.
All of those minor things quickly add up to massive amounts of stolen wages. For the employees, it is death by a thousand cuts. No single infraction is large enough to sue over, and no individual employee is going to bother going to court over $2 in unpaid wages. But when the company is doing it at scale, it means every employee is being paid less, which leads to massive illegal profits for the employer.
- Comment on When it was all trial and error 1 month ago:
The funniest one is the mushroom that makes you see tiny people for like a week. It’s not like psilocybin that causes different visuals depending on the person. As far as we can tell, the only visual hallucinations that these mushrooms produce are just… Tiny people. Like little Smurf-sized people on every surface, clinging to your clothes, climbing up walls, etc…
- Comment on Fact Check: **TRUE** 1 month ago:
Secondly cashapp patel said that the animal would also not be disqualified
Specifically, he said that current laws automatically disqualify both victims and perpetrators of sex crimes. For instance, both a pimp and his trafficked prostitute get charged with crimes. Kash said the law currently targets both parties. The senator then turned that around and went “so in cases of bestiality, the animal is the other party? And the animal could be hired by the FBI?” And Kash basically went “I mean… I guess if you want to put it like that?”
In reality, if a trafficking victim is being forced into bestiality, the animal wouldn’t be the “other party” in this case. The other party would be whoever is forcing the victim into doing it.
I dislike Kash, (he always looks like someone is slowly but steadily inserting hardboiled eggs into his ass, and he’s trying not to react to it), but as the above poster said, the actual reasoning behind the decision isn’t awful. Trafficking victims often get charged with sex crimes under our existing laws, because the laws don’t make a distinction between victim and perpetrator. Which then makes escaping the situation even harder because those arrests will show up on a background check when they apply for jobs. In that way, the system is actually designed to keep the victim in sex work, because it’s one of the few ways they’ll have to make money after being charged with a crime.
- Comment on There's so much cheating in Fortnite it's getting unplayable. 1 month ago:
Red Dead Online players: You mean cheating isn’t the expectation?
Seriously though, RDO had the single worst cheating problem I ever encountered. To the point that the multiplayer was downright unplayable unless you had cheats of your own. People would constantly troll with full-map aimbots, combined with infinite explosive ammo and no reloads. You log in, and your character is immediately taking an explosive bullet to the face on every single frame.
You start in a campsite where you can’t be damaged, but the sheer amount of explosions and particles being forcibly rendered are enough to make lower-end systems immediately lag. And as soon as you step outside of camp, you’ll take damage from those explosive rounds and immediately die. So at the very least, a godmode cheat is necessary just to be able to play the game without instantly dying.
- Comment on my year 1 month ago:
Yeah, this photo was actually one of the things that he credits with helping him get clean. Because this was basically rock bottom for him, and seeing this photo in tabloids was a large part of what made him realize how bad his addiction truly was.
He did the same thing that a lot of addicts do, and basically did a full 180 into health and fitness instead. Basically replaced the drug high with a workout high.
- Comment on Do analog triggers matter all that much? (In general and aside from racing games) 2 months ago:
Hah, I distinctly remember the first time I discovered the pressure sensitivity in MGS 3. I was hiding inside of a locker, and pressed a button to lean towards the grate and peek out. I lightly pressed it, and Snake barely leaned at all. I couldn’t really see what I needed to. So I mashed it harder. But I pressed it so hard that Snake slammed his face into the metal locker door with an audible thud. The noise alerted the guard and I was caught.
The fact that they even thought to program in a “slam face into whatever you’re peeking out of” mechanic has me rolling now that I’m thinking about it. It really is peak Kojima.
- Comment on Deans are so yesterday 2 months ago:
I guess we doin lean now
- Comment on when u stub ur toe on the coffee table 2 months ago:
My partner is a clutz, and I always joke that her Coffee Table Detector (little toe) is working great. It always earns me a death stare while she’s reeling, but being momentarily pissed at me is usually pretty effective at distracting her from the fact that her toe hurts.
- Comment on I think they're about to be in deanmand 2 months ago:
- Comment on Frog and Toad 2 months ago:
Hah, yup. In my head, I stupidly went “Milli is 10-3 so micro is 10-4.
- Comment on Frog and Toad 2 months ago:
It depends on how you’re doing it, (and how it was stored, because the molecule is pretty fragile and breaks down easily) but typically a single hit would be in the ballpark of 90-110 micrograms. So 500x would be about 5 grams. Which is a truly astronomical amount of LSD. Not the highest ever recorded, (that honor goes to a couple of idiots who thought it was cocaine and snorted it), but still a mind-meltingly high amount.
- Comment on CW: Mr. Breast 2 months ago:
He actually did a market study and realized that his videos with that smile on the thumbnail got more views. Like, a lot more. So he quietly started adding it into every thumbnail. He even went back to old videos are replaced the old thumbnails with ones that had that smile.
As for why that stupid smile makes his videos more popular? No clue. Kids are weird, and he does well in that demographic. So maybe it’s just a meme at this point. But the reason he’s known for that smile is ironically because it makes him more money.
- Comment on Has Piefed omitted some instances? 2 months ago:
That’s actually surprising, because lots of admins end up lumping the entire anarchist block of instances together.
- Comment on I guess they didn't Edge enough 2 months ago:
If F-18’s aren’t meant to be in the water, why does the navy keep throwing them into the ocean?